Fractional CISO Services · ANZ

Strategic cyber leadership.
Hands-on delivery.

Led by Doug Thompson · 20+ years in cyber security · AI-amplified for faster, sharper outcomes.

Board-ready governance, compliance delivery, and operational security leadership for Australian businesses — without the A$300K+ overhead of a full-time hire. We don't just write strategy; we step in and execute it.

Frameworks Essential Eight ISO 27001 NIST CSF Privacy Act & APPs PCI DSS Cyber Security Act 2024
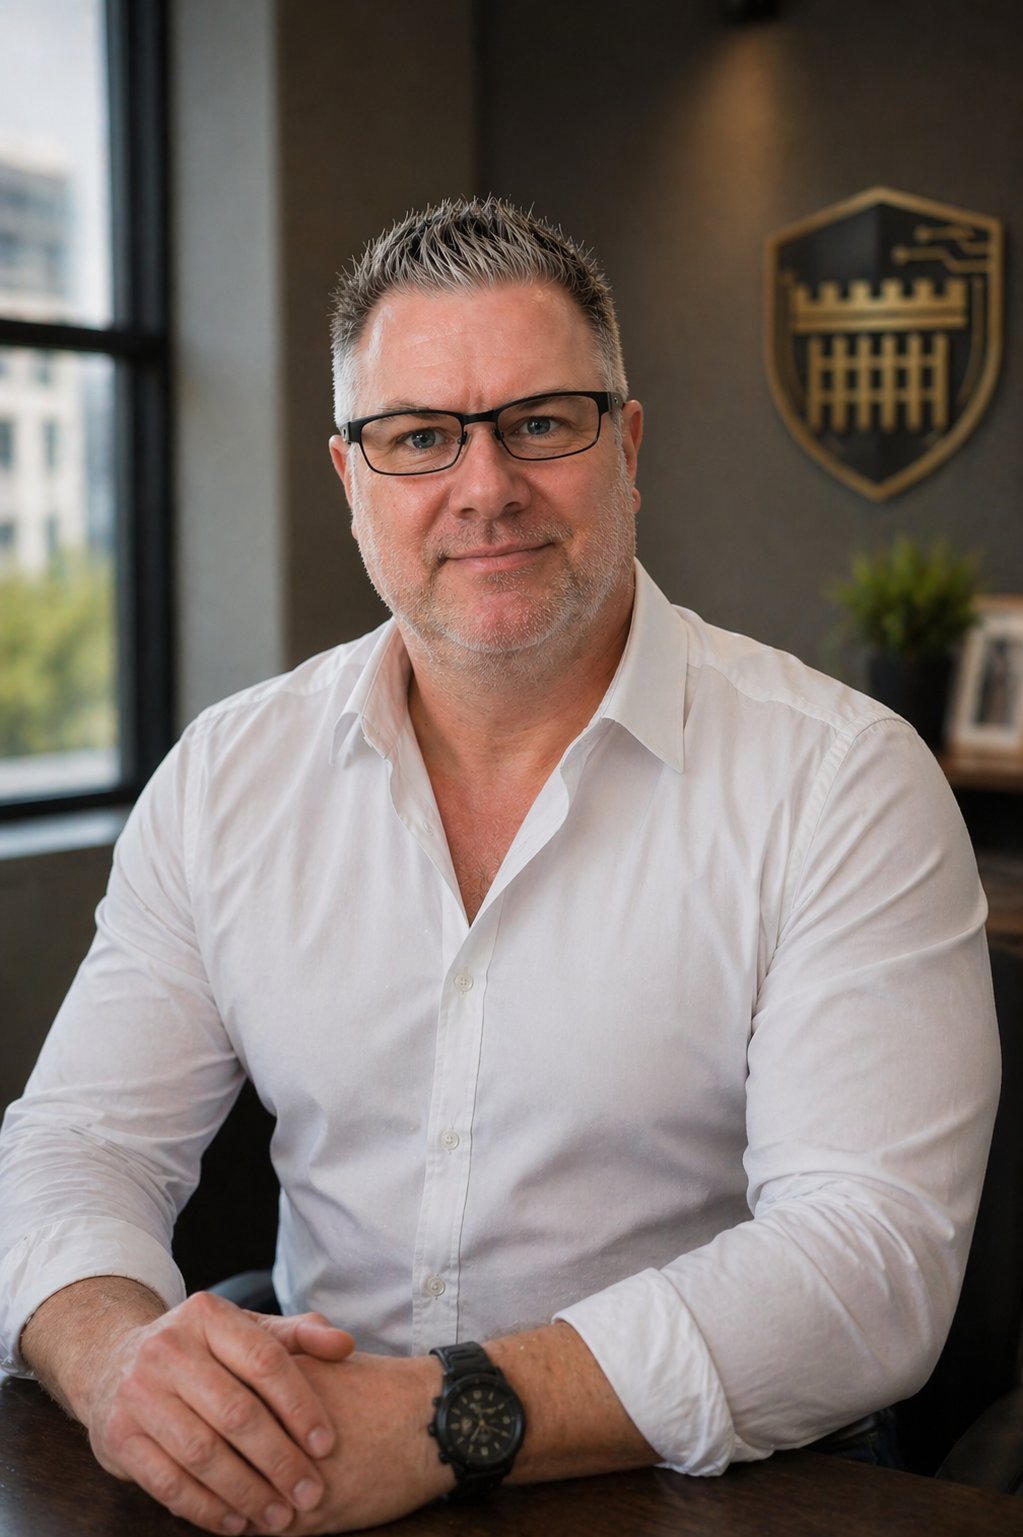
Doug Thompson - Founder, Portcullis Security
Doug Thompson
Founder & Principal CISO

With over 20 years in cyber security and more than 15 in executive security leadership, Doug has led security strategy, governance, incident response, and compliance programmes across complex enterprise environments.

He has sat at the executive table, presented cyber risk to boards, managed regulated compliance programmes, and built security teams from the ground up. His experience spans retail, financial services, SaaS & technology, healthcare, professional services, and critical infrastructure.

Portcullis Security exists because Doug saw too many growing Australian businesses exposed by the gap between needing a CISO and being able to hire one. This is hands-on operational leadership — not paper advisory from the sidelines.

Board-Level Reporting Incident Response Leadership Compliance Programme Delivery Security Architecture Team Building & Mentoring
Connect on LinkedIn

We don't sell tools, run a SOC, or do pen testing. We don't take on more clients than we can give genuine senior attention to. And we don't deliver paper advisory — if we can't own the outcome, we won't take the engagement.

Read more about our boundaries →

Two ways to work with me

Picking the right one matters more than what it costs. They solve different problems, on different time horizons.

Service Line One

vCISO Retainer — ongoing security leadership

A named CISO on your org chart, security documentation, and tender responses. Continuity, accountability, and someone there between sessions.

  • → Named CISO on your documentation
  • → Engagement cadence calibrated to context
  • → Board-ready reporting and risk ownership
See the four buyer profiles →
Service Line Two

Expert Days & Packages — project work, delivered

Defined scope, defined deliverables, fixed price for fixed scope, no ongoing commitment. Productised packages and day-based engagements.

  • → Cyber Health Check (lead offer)
  • → ISO 27001, Essential Eight, IR planning
  • → M&A diligence, post-incident recovery
See all packages →

Your next breach doesn't wait.
Neither should you.

Book a free 30-minute call with Doug. No obligation, no pitch deck — just an honest conversation about your security posture and what it would take to shore it up.

Book a Discovery Call